[Interview] “In the AI Era, State-Sponsored Hackers Are Moving More Stealthily”
IT DAILY ·
✦ AI Summary
At the SAS 2026 event in Bali, Indonesia, Kaspersky GReAT senior researcher Ryusojun was interviewed about AI-based hacking threats and the changes in Lazarus.
He explained that as AI spreads, the barrier to cyberattacks is falling, unsophisticated attackers can strengthen their capabilities, and it is becoming harder to trace the perpetrators.
Kaspersky said it has confirmed signs of Lazarus using AI and applying PQC in cases such as Operation FlashHole, and that countering vulnerabilities in financial security SW requires cooperation among the government, developers, and users.
BizCrushWant to follow Korean talks and live streams in real time?Try CapCrush on the web
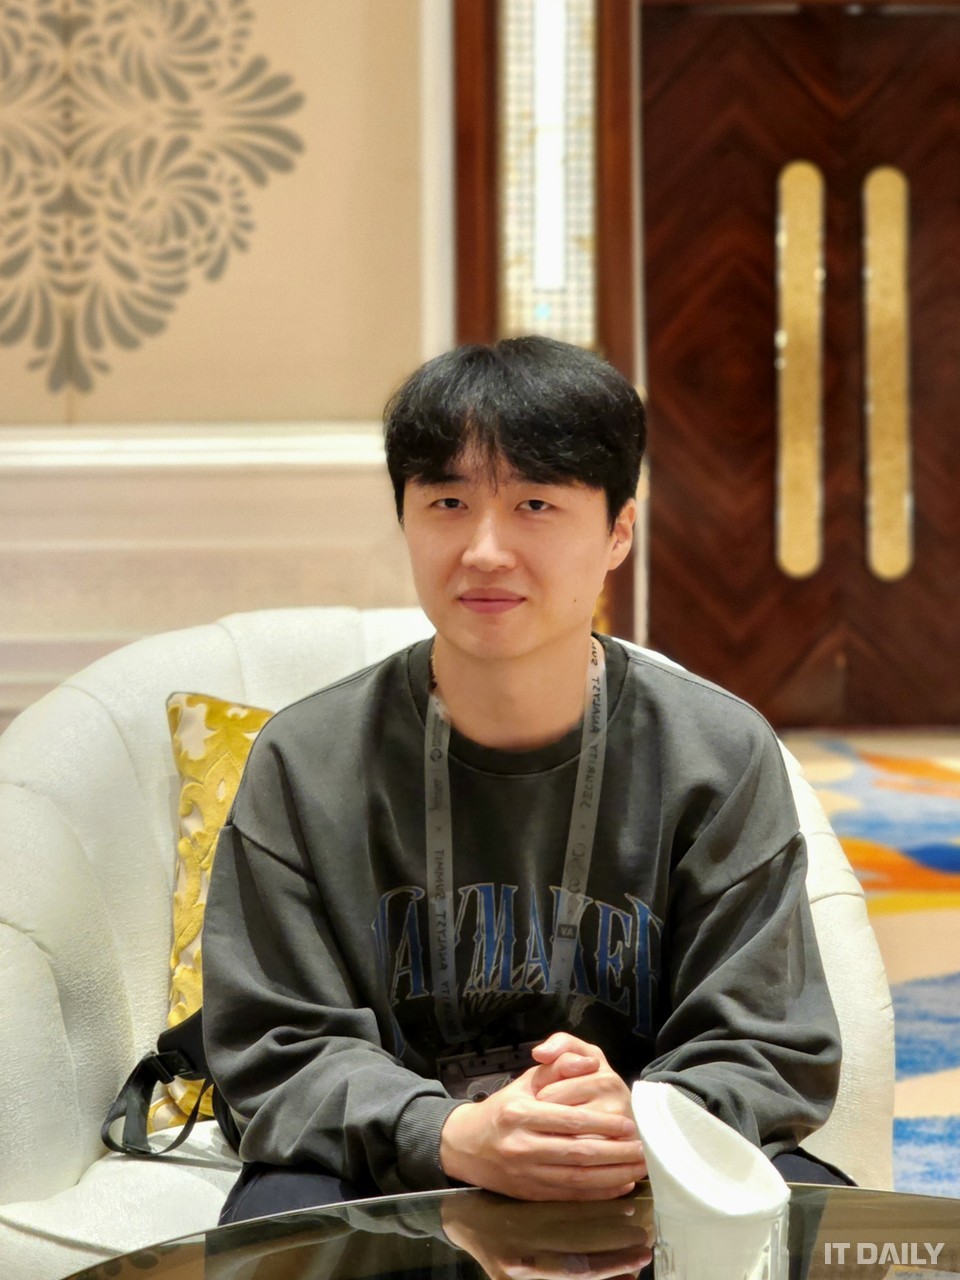
Last month, SAS 2026 was held in Bali, Indonesia. At the event, IT Daily interviewed Ryusojun, a senior security researcher on Kaspersky’s Global Research & Analysis Team (GReAT). Photo credit: Reporter Kim Ho-jun.
The interview focused on AI-based hacking threats and the evolution of the state-sponsored hacking group Lazarus. Ryusojun explained that as AI spreads, cyberattacks are becoming more democratized, making hacking possible for anyone.
Ryusojun also said that when a high-capability state-sponsored hacking group uses AI, its stealth and threat level increase further. He linked this trend to the changes seen in Lazarus, a state-sponsored hacking group.
As cases of ARTEX abuse have continued to emerge in South Korea and overseas, the security industry’s attention has turned to AI-automated attacks. ARTEX is an AI autonomous penetration testing tool that connects with external LLMs. The tool can automatically conduct reconnaissance, search for vulnerabilities, and design attack paths. As ARTEX has also been abused in recent financial-sector intrusion incidents, the controversy surrounding its misuse is growing.
Ryusojun assessed that this trend is lowering the barrier to cyberattacks. Even unsophisticated attackers who previously used public hacking tools can now strengthen their offensive capabilities with AI. As AI makes it possible to generate attack code without specialized knowledge, attack patterns are also becoming less structured. Ryusojun explained that this is making it more difficult to track and identify the perpetrators.
Although attention is now concentrated on AI-automated hacking issues, Ryusojun advised that cyberthreats do not unfold in only one direction. While noting that AI-based attacks are increasing, he said defenders also need to be wary of becoming overly fixated on a single issue.
Ryusojun stressed that even as AI hacking spreads, state-sponsored hacking groups’ advanced persistent threats (APT) must also remain a concern.
Based on Kaspersky’s tracking results, Ryusojun said signs of AI use have been detected not only in Lazarus but also in other Korean-language-speaking attack groups such as Kimsuky and BlueNoroff. Their AI use includes malware development, lure file creation, and fake website creation. He explained that these groups aim to steal information while remaining undetected for long periods.
Ryusojun said that given these goals, the potential for covert AI use is high. The gist of the article’s subheadline is: an evolved Lazarus, AI use, and PQC concealment.
A case Kaspersky recently disclosed is Operation FlashHole. In Operation FlashHole, traces of AI use by an attacker believed to be Lazarus were found. The attacker used a GitHub page created in September last year, and the page’s posts were disguised as a resume for a senior network equipment developer. AI-generated profile photos and a targeted fake website were used to lure victims.
Operation FlashHole began in July last year. The damage from Operation FlashHole is believed to involve at least three companies in South Korea in the construction, software (SW), and wired telecommunications equipment manufacturing sectors. This was not the first case; FlashHole was presented as an extension of Operation SyncHole, which Kaspersky discovered last year.
Both attacks targeted South Korea, and signs that domestic SW was abused were confirmed in both cases. In addition, the malware preferred by Lazarus, LPEClient, was used in both attacks.
The difference lay in the sophistication of the attack method and the level of concealment. The main method in previous attacks was infection through websites such as media outlets, which falls under the Watering Hole type. A Watering Hole attack involves taking control of a website frequently visited by the target and then inserting malware.
By contrast, FlashHole took the approach of directly reaching targets through spear-phishing emails. The aim was to raise the success rate of the attack. FlashHole used targeted phishing to deceive victims and then lured them to a fake website for Watering Hole attacks, while also additionally using two undisclosed new tools, TouchHub and ClientHub.
The latest LPEClient strengthened its functions to run additional malware directly in memory and neutralize the monitoring features of security solutions to evade detection. For communication encryption, it applied the post-quantum cryptography (PQC) algorithm ML-KEM-1024, increasing both stealth and communication protection. According to Kaspersky’s analysis, Lazarus is believed to have begun adopting PQC more than a year earlier, around September 2024, well before the time of this disclosure.
Ryusojun said that if a domestic relay point is used as a command and control (C2) server, communication records could be exposed and collected, and explained that the intent behind applying PQC is to block the risk of decrypting communications collected in the past in a future quantum-computing environment. Describing the risk as “collect first, decrypt later,” he said this can be seen as a move to prevent that outcome, even if it is not an immediate concern, and he added that Lazarus continues to update its detection-evasion features while pouring significant technical effort into the malware LPEClient.
In both FlashHole and SyncHole, web authentication and security SW widely used in financial sectors and other areas were identified as the initial intrusion path. After reviewing the overall attacks, Ryusojun said he places more weight on the possibility that infection started from financial security SW.
However, Ryusojun said no direct abuse code or vulnerabilities themselves have been confirmed. Accordingly, he maintained a cautious view while also explaining the possibility that JavaScript embedded in a website triggered a potential vulnerability.
As background to this judgment, the structural vulnerability of financial security SW has long been repeatedly raised as an issue. A joint research team from Theori, Korea University, KAIST, and Sungkyunkwan University presented related findings in a paper accepted last June by the international security conference USENIX Security 2025.
The study found 19 vulnerabilities in essential domestic financial and security programs. The researchers pointed out that these programs run on local PCs outside the browser with high privileges, trust web page API requests excessively, and neglect their own root certificate management. As a result, they said, keystroke theft and abuse for RCE are possible.
In July this year, the National Intelligence Service, the National Police Agency, and KISA jointly issued a cybersecurity advisory, mentioning targeted attacks aimed at financial security SW. According to the advisory, state-sponsored hacking groups took control of websites and then used the compromised sites as a Watering Hole attack vector. It also said they abused security programs for use on specific websites, such as digital signature, security authentication, and keyboard security programs, and used them as a means of distributing malware when the security programs were not up to date.
Ryusojun said a multilateral response is needed to resolve these issues. He explained that government-led institutional improvements are necessary, developers must respond to SW vulnerabilities, and users must manage updates. He added that no single party can solve the problem on its own, and that cooperation among all stakeholders in line with their respective roles is the condition for maintaining cybersecurity.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=243097
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.
Keep reading
BizCrush