PHP Vulnerability Reverberates, With Additional Linked Attack Cases Emerging
IT DAILY ·
✦ AI Summary
CISA added the Linux kernel vulnerability CVE-2026-46300, which is being exploited in connection with PHP2Shell (CVE-2026-109618·109619), to the KEV list and urged patching.
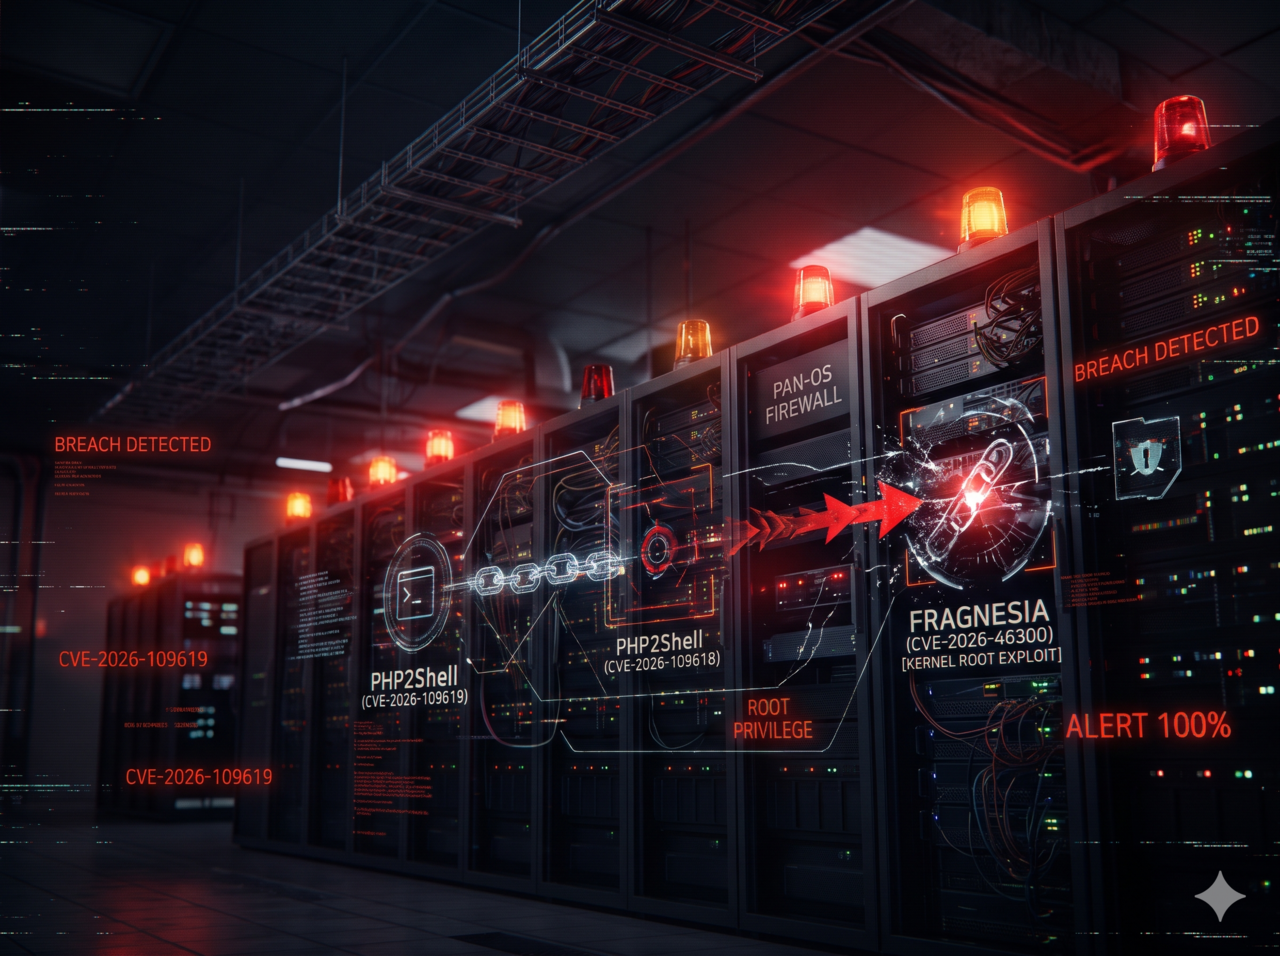
DREAM said an attacker simultaneously exploited PHP2Shell and Fragnesia to target Palo Alto Networks' PAN-OS firewalls.
The attacker used a single HTTP request to gain administrative privileges and install web shells, then deleted logs and erased traces.
As the fallout from PHP2Shell (CVE-2026-109618·109619) continues, reports say attacks linking the existing vulnerability with PHP2Shell have emerged. Overseas outlets, including Bleeping Computer, reported on the 30th that the expansion of these linked attacks is also raising the level of risk.
In response, the Cybersecurity and Infrastructure Security Agency (CISA) issued an alert for federal agencies. CISA urged patching a Linux kernel vulnerability that is being exploited in connection with PHP2Shell.
The vulnerability in question is CVE-2026-46300. Its alias is Fragnesia, and it was discovered in May this year.
Fragnesia is known as a variant of Dirty Frag, a high-risk Linux kernel vulnerability. It can be exploited by ordinary users, and if abused, it can allow arbitrary memory manipulation. It can also lead to full administrative privilege compromise.
The U.S. cybersecurity agency CISA added 'CVE-2026-46300' to the KEV list on the 28th. KEV indicates that actual exploitation by attackers is underway. The notable point of this action is the PHP2Shell-Fragnesia connection.
In Fragnesia's KEV description, CISA warned of links with 'CVE-2026-109618·109619.' It said that the connection could enable PHP web shell installation and also allow root-privileged command execution. This is tied to the pattern in which attackers compromise systems by chaining different vulnerabilities together.
However, CISA did not disclose details of how PHP2Shell and Fragnesia are linked. As a clue to the attack pattern, a report released on the 26th by Israeli cybersecurity company DREAM was cited.
According to DREAM's report, the attacker simultaneously exploited the remote code execution vulnerability PHP2Shell and the privilege escalation vulnerability Fragnesia to target firewalls based on Palo Alto Networks' PAN-OS. PAN-OS is the OS used in Palo Alto Networks products.
The attack first targeted the firewall's management web server, triggering a memory error by flooding it with large volumes of data. The attacker then used the gap created by that memory error to secure an entry path through PHP2Shell before exploiting Fragnesia inside the OS. As a result, the attacker altered a configuration file so that administrator password verification would always be bypassed, and DREAM said the entire process took about 15 minutes to complete.
Chaining multiple vulnerabilities in an exploit is a basic tactic in cyberattacks. What set this case apart, however, was that it was carried out in a single HTTP request. The attacker carefully selected the target in advance and launched the attack in a short period of time.
DREAM's report has been released. The attacker built the attack environment with DeepSeek, then scanned about 19,000 PAN-OS devices exposed to the internet and selected 240 firewalls running vulnerable versions. The selected countries were the United States, Japan, Taiwan, and South Korea.
The attacker first struck firewalls at U.S. government agencies and then carried out additional attacks against the remaining targets. As a result, web shells were installed on 24 firewalls in about 3 hours and 40 minutes, and the attacker chained PHP2Shell and Fragnesia using the web shell footholds. The attacker then gained administrative privileges, collected user information, and attempted to create backdoor accounts.
Later, late on the 24th, the attacker deleted forensic logs and other traces of the attack in an apparent effort to evade tracking. However, the operation was concluded with attack web shells and other tools still left behind for future use.
In connection with this case, Palo Alto said in an announcement on the 29th that exploitation of the PHP2Shell vulnerability is underway against PAN-OS systems with management interfaces exposed to the internet. It also advised blocking internet access to management interfaces immediately if such access is allowed and urged applying PAN-OS security updates.
The Korea Internet & Security Agency said on the 29th, Korea time, that some Palo Alto products require security updates, and recommended applying security updates as a response measure after identifying product lines affected by a specific vulnerability. The recommendation applies to PAN-OS versions affected by the PHP2Shell vulnerability, limited to versions 10.2, 11.1, 11.2, 12.1, and 12.2.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=242587
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.