Zscaler Announces Enhanced Zero Trust Deception Solution Tailored to Advanced AI Threats
TECHWORLD ·
✦ AI Summary
Zscaler announced that it is strengthening an integrated defense solution combining Zscaler Deception and ZPA to respond to advanced attacks using AI.
CSA held an emergency strategy briefing to prepare for the AI Vulnerability Storm and presented building deception capabilities within 90 days as one of 11 key priorities.
Zscaler said it provides a solution for existing ZPA customers that automatically Revoke private app access rights when a decoy is detected, without additional hardware or agents.
Zscaler announced that it is strengthening an integrated defense solution that combines Zscaler Deception and ZPA to respond quickly to advanced attacks using AI. The target of this response is Mythos-level AI threats, and the goal is immediate response.
Meanwhile, CSA held an emergency strategy briefing to prepare for the AI Vulnerability Storm, with more than 250 CISO and security experts in attendance, including former CISA, NSA, and White House cybersecurity leaders. CSA designated “build deception capabilities within 90 days” as one of 11 key priorities and presented it as a HIGH risk item. It also recommended adopting deception technology regardless of the attack tool or vulnerability type, saying that deception can immediately capture an attacker’s TTP.
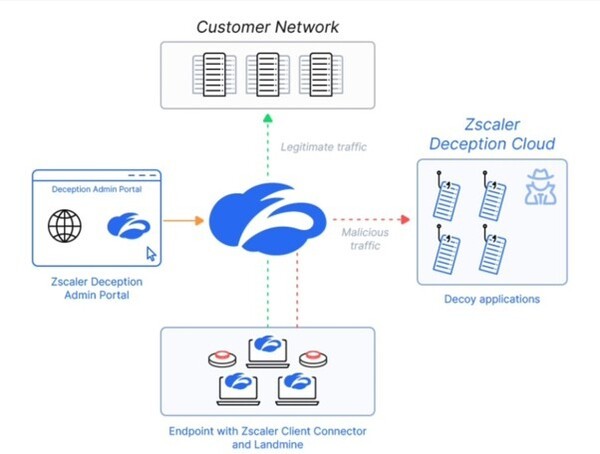
Zscaler is offering the solution to existing ZPA customers. The solution requires no network reconfiguration, no additional hardware installation, and no additional agent installation. It also helps organizations embrace and activate deception strategies across their Zero Trust environment with just One-click.
AI-based attacks use legitimate tools and can complete the Kill Chain in a matter of minutes. As a result, signature- and behavior-based detection solutions such as EDR have limitations in responding. Zscaler Deception decoys are designed so that no legitimate user ever accesses them, and any interaction with a decoy is treated as a 100% threat signal, a Deterministic Alert with no False Positive.
Once a decoy is detected, ZPA is triggered immediately. Private app access rights are automatically Revoke from every device the user is connected to, and no manual approval process from a security analyst is required. This process applies preapproved automated response actions to block attacks immediately, delivering real-time blocking in step with the speed of AI attacks without relying on SOC response wait times.
Rottelc CEO Jo Won-gyu said that, unlike CSA's 90-day deception deployment task, it can be implemented in just a few minutes for Zscaler customers. He added that the effect of building deception capabilities is that both AI-based Agentic attackers and internal intruders can be clearly detected and isolated, helping protect the company's core assets.
Source: TECHWORLD · Kim Gyeong-ju
Original: https://www.epnc.co.kr/news/articleView.html?idxno=408443
References
This article was produced with the help of an automated content generation algorithm.
Source: TECHWORLD
View originalThis article was summarized and organized by BizCrush based on the original article from TECHWORLD. For exact quotations and full details, please refer to the original article.