S2W Delivers Talk at VB Conference for Sixth Straight Year, Spotlighting Supply Chain Attacks Targeting Security Researchers
IT DAILY ·
✦ AI Summary
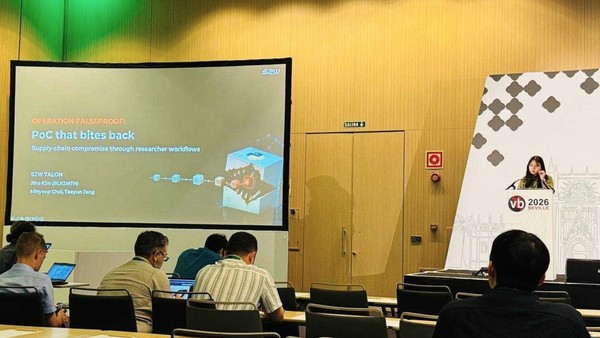
S2W said that at VB2026, Senior Researcher Kim Ji-ho of its Integrated Analysis Lab delivered an invited talk and presented the company's research findings.
The presentation shared a software supply chain attack case in which PoC code for a security researcher's vulnerability verification was abused as a malware infection path.
S2W also introduced AI-based detection technology that analyzes package information, dependency structures, and anomalous signs in native extension modules.
S2W has presented its research findings every year at the global security academic event known as the Virus Bulletin (VB) Conference, and this year marked its sixth consecutive presentation. According to S2W's presentation disclosed on the 20th, Kim Ji-ho, senior researcher at S2W's Integrated Analysis Lab, delivered an invited talk at VB2026. VB2026 was held from the 14th to the 16th in Seville, Spain, local time.
S2W has continued analyzing North Korea-linked hacking groups and dark web threat actors, and this presentation also covered work that extended that research. In particular, this year it shared cases of software supply chain attacks that exploited security researchers' vulnerability verification processes. Senior researcher Kim Ji-ho presented a case in which PoC code for vulnerability verification was abused as a path for malware infection.
In this presentation, S2W also shared AI-powered detection technology along with the attack case. As a result, the presentation covered both a supply chain attack aimed at security researchers and AI-based technology for detecting it.
The VB Conference is a cybersecurity academic event hosted by Virus Bulletin, a UK-based organization specializing in security information, testing, and certification, and it began in 1991. Researchers, corporate security leaders, incident response teams, government officials, and law enforcement personnel from various countries take part in the event, where they share malware analysis, threat intelligence research, and case studies from real-world investigations.
S2W has presented at the event for six consecutive years, from 2021 through this year. S2W has presented changes in attack strategies used by North Korea-linked hacking groups based on real cases, tracking of deep web and dark web threat actors, and analysis of mobile malicious apps, and this year it expanded its presentation scope to supply chain security beyond its previous themes. This year, S2W analyzed how code for security research and related packages were turned into attack vectors.
On the third day of the event, Senior Researcher Kim explained cases in which proof-of-concept (PoC) code for vulnerability verification was abused as a malware infection path. According to the presentation, the attacker copied a publicly available legitimate PoC and tampered with dependency settings, while also modifying some auxiliary code. As a result, when the researcher prepared the development environment, the malicious package was installed at the same time, and when the PoC was later executed, that package was invoked, triggering an infection chain in which a malicious native extension module hidden inside the package was activated.
Senior Researcher Kim introduced the process from the start of the attack to the execution of the malware, while also presenting a detection system for identifying malicious packages in advance. The detection system is a technology that automatically analyzes package information, dependency structures, and anomalous signs in native extension modules, and uses AI to interpret evidence in high-risk cases.
Senior Researcher Kim said that software supply chain attacks have become sophisticated enough to exploit even security researchers' routine vulnerability verification processes as attack paths. He added that S2W will continue in-depth analysis of real-world attack cases and research into AI-based detection technology, contributing to the rapid identification of new attack techniques and to improving practical response capabilities.
Source: IT DAILY · Lee Jae-young
Original: https://www.itdaily.kr/news/articleView.html?idxno=242302
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.