P&P Secure Supplies Integrated Account Management Solution to Major Domestic Conglomerate
IT DAILY ·
✦ AI Summary
P&P Secure said on the 17th that it had completed the deployment of its integrated account management solution, DBSAFER IM, for a major domestic conglomerate.
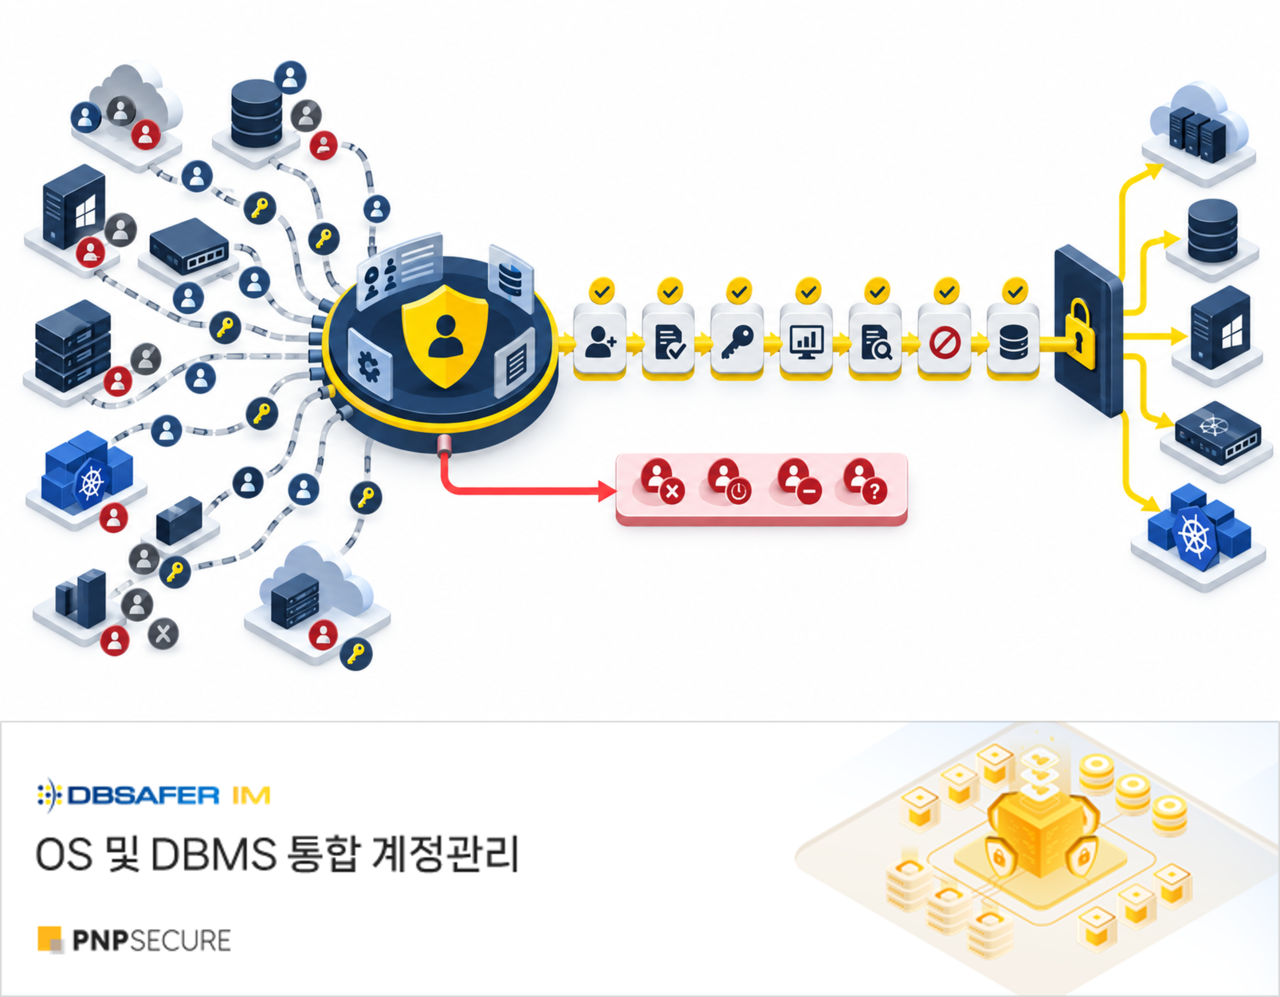
With this deployment, the conglomerate can centrally manage accounts and permissions distributed across DBMS, OS, and network devices.
The deployment scope also included the Kubernetes environment, and accounts in container and cloud-native infrastructure were designed to be managed under the same policy.
P&P Secure announced on the 17th that it had completed the deployment of its integrated account management solution, DBSAFER IM, for a major domestic conglomerate. The deployment target is a major domestic conglomerate in South Korea.
Large-scale IT environments tend to leave accounts and permissions fragmented. Separate accounts are created for each DBMS, OS, and network device, and when administrators or outsourced staff change, residual privileges often remain or revocation is delayed.
When cloud and container (Kubernetes) environments are added, accounts are created and deleted dynamically. As a result, it becomes even harder to keep track of account status in cloud and container (Kubernetes) environments.
With this deployment, the major domestic conglomerate can now centrally manage accounts and permissions distributed across DBMS, OS, and network devices through DBSAFER IM.
The project focused on centralizing the management of accounts distributed across multiple devices. By introducing DBSAFER IM, the conglomerate established a centralized management system for accounts scattered across DBMS, OS, and network devices.
To do this, DBSAFER IM provided functions for managing account creation, modification, and deletion, as well as granting and revoking privileges. It also supported permission control based on request, approval, and authorization procedures, collection and synchronization of information from heterogeneous devices, identification of unauthorized and expired accounts, control of privileged account use, policy-based password management, and automatic access functions. Policy-based password management and automatic access functions also reduced the risk of account exposure.
The deployment scope also included the Kubernetes environment. Accordingly, accounts created in container and cloud-native infrastructure were designed to be managed under the same policy, making this a case of integrated management under a single standard that extended beyond the existing DBMS- and OS-centered scope to Kubernetes and cloud environments.
Kim Min-gyu, head of P&P Secure's corporate business division, said that the larger the IT environment, the more severe the fragmentation of accounts and permissions becomes. He added that this deployment is a case of integrated management under a single standard across DBMS, OS, and cloud environments such as Kubernetes. He also said the company plans to continue supporting customers in unifying distributed accounts and permissions and managing auditable histories.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241673
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.