KISA Pushes a Full-Cycle Ransomware Response Strategy, Strengthening Recovery and Recurrence Prevention Measures
IT DAILY ·
✦ AI Summary
KISA unveiled a full-cycle response strategy to address rising ransomware damage.
The strategy focuses on recovery and system normalization after reporting, as well as recurrence prevention.
Reports in the first half of this year totaled 145, up 76.8% from 82 in the same period last year.
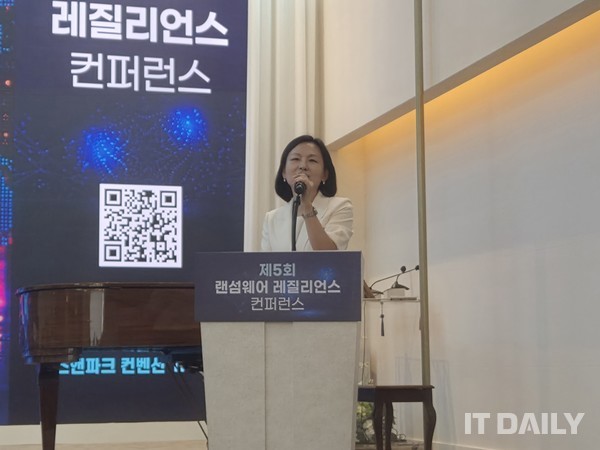
The Korea Internet & Security Agency (KISA) has established and released a new strategy to respond to rising ransomware damage. KISA announced the plan at the 5th Ransomware Resilience Conference held on the 16th at Peace & Park Convention in Yongsan-gu, Seoul. The presentation, delivered by Lee Dong-yeon, head of KISA's Public Damage Response Division, introduced the full-cycle ransomware response strategy.
The new strategy focuses on helping affected companies restore systems quickly after reporting an incident. KISA designed the strategy to ensure that companies can move from reporting damage to recovery and normalization. It includes measures to strengthen ransomware analysis and recovery, as well as recurrence prevention.
KISA received 145 reports from companies hit by ransomware in the first half of this year. That was up 76.8% from 82 reports during the same period last year. Based on the current trend, the number could surpass last year's full-year total of 274 by the end of the year.
KISA also mentioned the emergence of attacks abusing AI. As a result, concerns have been raised that the scale of damage could expand in the future. KISA unveiled the full-cycle ransomware response strategy to address such circumstances.
In February, KISA created a "Ransomware Response Team" to handle ransomware incidents. Then in March, it launched the "Ransomware Full-Cycle Response Task Force" with 15 experts from academia, industry, research institutions, and government. The task force held five regular monthly meetings and, through that process, identified key tasks for each ransomware response stage.
The strategy prepared by the task force is organized into five stages: damage prevention, analysis and response, recovery support, immunity strengthening, and organization apprehension. The strategy covers the full cycle of ransomware response. Detailed tasks include backup restoration drills, preventive measures using self-diagnosis tools, stronger detection capabilities, rapid recovery, and recurrence prevention.
KISA placed special emphasis on recovery. Under the current Network Act, reports must be filed within 24 hours of recognizing a breach incident, but if an affected company fails to recover ransomware quickly after filing, the damage can spread. KISA therefore aims to close the response gap between reporting and business normalization, while focusing on damage recovery strategies and recurrence prevention measures.
The government and KISA are moving ahead with efforts to respond to cyberattacks accelerated by AI. To that end, they plan to design a standard schema specialized for ransomware and collect and share attack signs and breach information in a consistent format to speed up detection and response. They also plan to secure data for decryption recovery and diversify detection capabilities for a range of scenarios, so that they can determine on site whether recovery is possible when ransomware is reported. These steps are meant to improve response speed, and companies were also urged to report incidents quickly.
In fact, two companies that reported ransomware damage to KISA this year successfully recovered encrypted data. The two companies did not pay the hackers' total ransom demand of KRW 770 million and also managed to restore operations.
Lee said these cases show that reporting and preserving evidence are effective in reducing damage. He explained that the two companies reported immediately to KISA while preserving data after discovering the infection, which allowed KISA to collect samples and generate recovery keys. He added that cases of failure to recover even after paying ransom are common, and said it is more effective to seek help from institutions such as KISA.
KISA is not limiting its ransomware response to recovery, but is also pushing to strengthen coordination with investigative agencies. KISA plans to share data and clues obtained through ransomware analysis with law enforcement, with the aim of helping apprehend cybercrime organizations. In addition, it plans to reflect investigative results in ransomware recovery technologies and policies.
KISA will promote the ransomware full-cycle response strategy in stages over the medium to long term. From this year through next year, the focus will be on supplementing existing measures and strengthening on-site response capabilities. It will also begin work on schema design and ransomware recovery tool development in the second half of this year.
By 2029, it aims to concentrate on strengthening AI-linked recovery and immunity systems, and by around 2030 it plans to establish a national resilience ecosystem that is not shaken by ransomware. KISA President Lee Sang-jung said ransomware damage is spreading worldwide. He also stressed the need for an organic response covering prevention, recovery, and recurrence prevention, and said the agency will further flesh out an operational framework that can work effectively in the field.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241662
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.