RedPenSoft Registers 'XSCAN Server Runtime' on Public Procurement Service's KONEPS
IT DAILY ·
✦ AI Summary
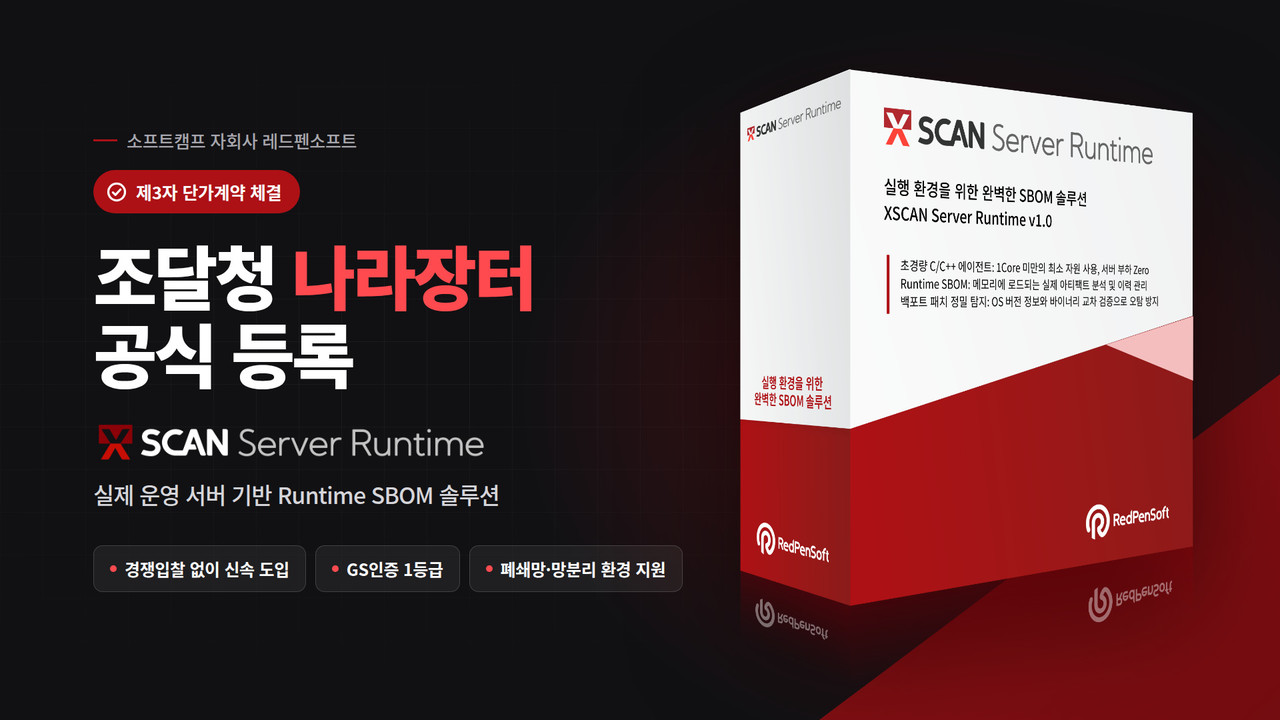
SoftCamp announced on the 15th that it had signed a third-party unit price contract with the Public Procurement Service and registered the server security solution XSCAN Server Runtime, operated by its subsidiary RedPenSoft, on KONEPS.
With this listing, public institutions and local governments will be able to purchase and adopt XSCAN Server Runtime through KONEPS without a separate competitive bidding process.
XSCAN Server Runtime identifies SW installed on servers in operation and currently running components to generate a runtime SBOM, and it selects vulnerabilities by analyzing each server's execution status and change history.
SoftCamp announced on the 15th that it had signed a third-party unit price contract with the Public Procurement Service and registered the server security solution "XSCAN Server Runtime," operated by its subsidiary RedPenSoft, on KONEPS.
SoftCamp said the KONEPS listing will allow public institutions and local governments to purchase and adopt XSCAN Server Runtime through KONEPS without a separate competitive bidding process.
The developer of XSCAN Server Runtime is RedPenSoft, while SoftCamp is responsible for the KONEPS listing and supplying the product to the public sector.
The announcement came as recent SW supply chain attacks have been increasing, alongside criticism that a "SW Bill of Materials (SBOM·Software Bill of Materials)" prepared during the development and delivery stages is not enough. As a result, the need for continuous verification of SW running in operating environments and of the impact of vulnerabilities has been raised.
XSCAN Server Runtime identifies SW installed on servers in operation and identifies currently running components to generate a "runtime SBOM (SW inventory at runtime)." It also analyzes the execution status of each server and change histories to select vulnerabilities that are likely to have a material impact in operating environments.
The solution can be built for public and financial institutions with closed-network environments in mind, and it can also be built with network-segregated environments in mind. In addition, it allows key assets and analysis information to be directly controlled within the company's own environment.
SoftCamp CEO Bae Hwan-guk said the KONEPS listing of XSCAN Server Runtime marked an opportunity to expand SoftCamp's public-sector business in SW supply chain security. He added that the company will support this effort based on RedPenSoft's experience and technical capabilities in financial, public, and private-sector deployments, and said it is committed to helping customers identify and manage SW risks in their operating environments.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241615
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.