LavaWave Overhauls Its Website to Focus on Protecting Bodycam Phishing Victims
TECHWORLD ·
✦ AI Summary
LavaWave announced on the 7th that it had fully revamped its website.
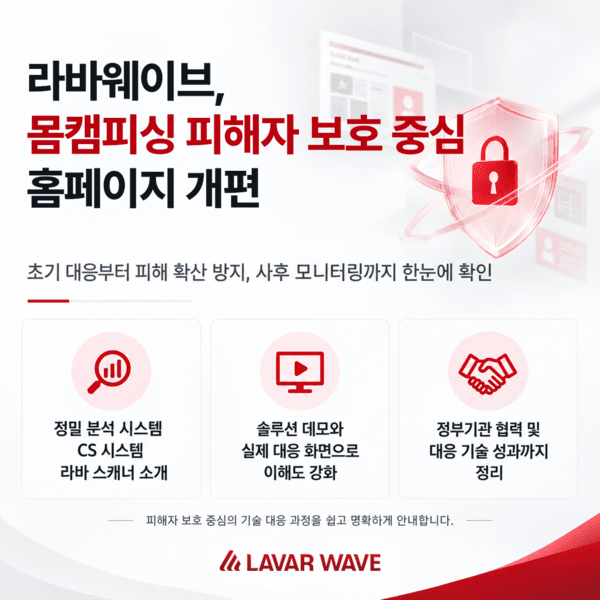
The redesign was structured around protecting bodycam phishing victims so users can see initial response through post-incident monitoring at a glance.
The website introduces 4 types of criminal approaches, 3 systems and a total of 8 modules, as well as a solution demo and anonymized analysis screens.
LavaWave announced on the 7th that it had fully revamped its website. The redesign centers on protecting bodycam phishing victims, and the site has been structured so users can see everything from initial response to post-incident monitoring at a glance.
The redesign was aimed at making the actual response process easier to understand from the victim’s perspective. On the website, LavaWave visualized four types of criminal approaches that are actually reported: random matching chat, open chat rooms, SNS DM, Telegram, and impersonation of foreigners. Through this, it sought to improve understanding of how the crime escalates into extortion.
LavaWave also presented the technologies it uses in its response. Its technology introduction has been structured into 3 systems and a total of 8 modules, and the 3 systems are the precision analysis system, CS system, and Lava Scanner.
The precision analysis system is designed to identify data exfiltration routes and attacker infrastructure through malicious file and APK reverse analysis, as well as execution-process and external communications analysis functions. Based on data injection and dummy data insertion functions, the CS system provides an integrated defense function that lowers the likelihood that a victim’s real acquaintance will be targeted and delays extortion and distribution attempts.
Lava Scanner added an identification function that applies automatic detection of web and SNS distribution indicators, as well as similarity detection technology based on comparison with originals for cropped, compressed, and color-corrected altered images and videos. It also linked up with the protection app 'LAVAR X,' which detects and removes malicious apps and disguised codecs. Through this, it has built a continuous integrated response system spanning analysis, spread response, and post-incident monitoring based on Lava Scanner and 'LAVAR X.'
It also strengthened the 'Solution Demo' menu to help victims better understand the service, allowing them to directly see how data injection, dummy data, and Lava Scanner work in that menu. In addition, it anonymized and released the isolated analysis environment and packet analysis screens used in actual response operations.
Source: TECHWORLD · Kim Hye-jin
Original: https://www.epnc.co.kr/news/articleView.html?idxno=406633
References
This article was produced with the help of an automated content generation algorithm.
Source: TECHWORLD
View originalThis article was summarized and organized by BizCrush based on the original article from TECHWORLD. For exact quotations and full details, please refer to the original article.