LG U+ teams up with HackerOne to launch global bug bounty program
IT DAILY ·
✦ AI Summary
LG U+ said it will begin operating a global bug bounty program on the 24th in partnership with HackerOne, targeting all service areas, including mobile, internet, and enterprise services.
The program will allow only global white hat hackers who have passed identity verification and capability screening to participate, while accepting reports on an ongoing basis and running threat detection and vulnerability analysis and improvement procedures.
LG U+ has jointly operated a bug bounty system with KISA since October 2024, and said this partnership will help it proactively identify and address undiscovered vulnerabilities in response to the expansion of overseas infrastructure touchpoints.
LG U+ said it will begin operating a global bug bounty program on the 24th in partnership with HackerOne, covering all LG U+ service areas, including mobile, internet, and enterprise services. A bug bounty is a system that pays rewards to white hat hackers who discover security vulnerabilities in services and IT infrastructure.
As AI advances, security threats are increasingly crossing borders, and the overseas infrastructure links of telecom services are also expanding into areas such as roaming, cloud, and AI services. As a result, the need to respond to global security threats is growing.
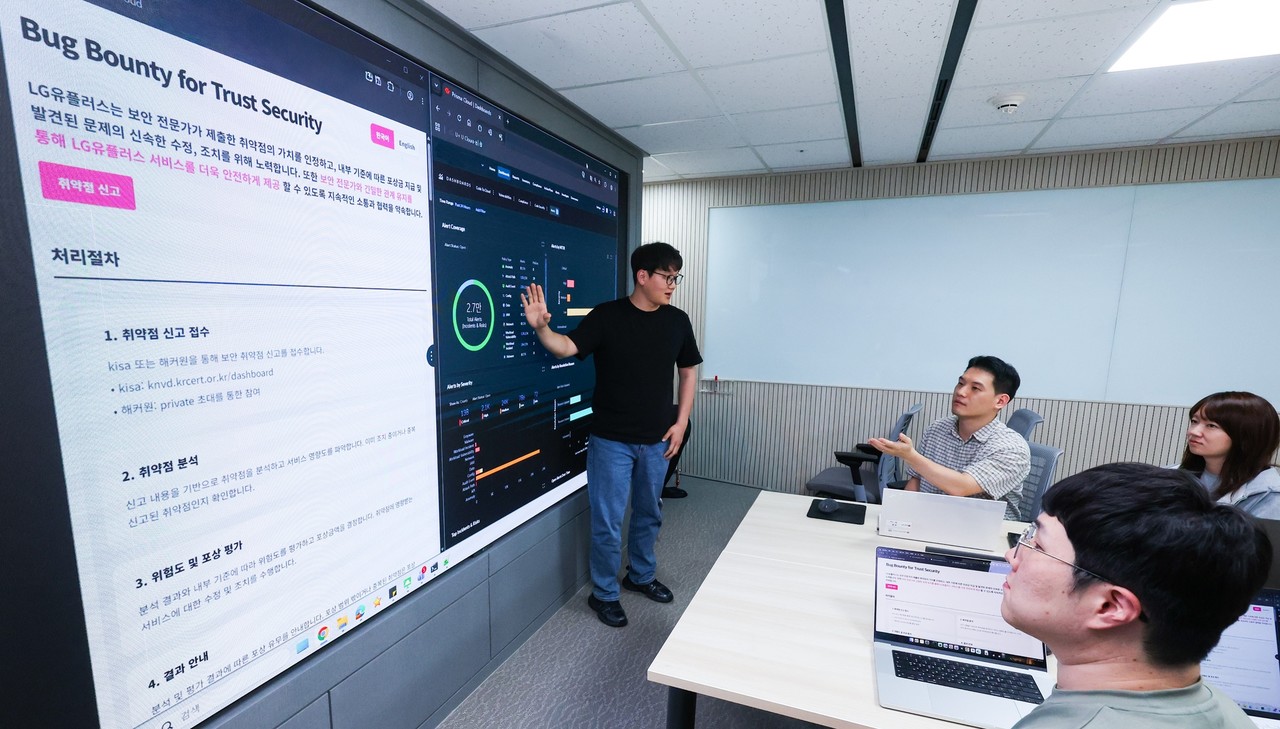
The accompanying photo shows information security staff discussing the operation of the global bug bounty program.
LG U+ launched the global bug bounty program after signing a partnership with HackerOne, a global bug bounty platform company, to proactively address potential security risks. HackerOne is a global bug bounty platform with more than 2.4 million white hat hackers around the world participating, and it has long-term partnerships with numerous global big tech companies, including the U.S. Department of Defense.
The program will operate with only global white hat hackers who have passed identity verification and capability screening. LG U+ accepts reports from global white hat hackers on an ongoing basis.
Based on the reports received, the program will operate through parallel threat detection and rapid vulnerability analysis and improvement procedures. Through this, LG U+ plans to proactively respond to potential security risks.
Since October 2024, LG U+ has jointly operated a bug bounty system with the Korea Internet & Security Agency (KISA). Separately from the KISA joint operation, the company said it will run a HackerOne global program to identify vulnerabilities and management blind spots, and said this partnership will secure a vulnerability management system that meets global standards.
Hong Kwan-hee, head of LG U+'s Information Security Center and CISO, cited the growing scope of telecom services connected to overseas infrastructure as the backdrop to this partnership, and said the goal of the partnership is to proactively identify and address undiscovered vulnerabilities in response to the expanding contact points between telecom services and overseas infrastructure. He added that the company will work to create a safe and transparent security ecosystem and lead the spread of a responsible vulnerability management culture.
Source: IT DAILY · Seong Won-young
Original: https://www.itdaily.kr/news/articleView.html?idxno=241154
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.