Hacking Server Behind Shinhan Bank Breach Found to Contain Traces of Chinese-Language AI Tool
IT DAILY ·
✦ AI Summary
In relation to the Shinhan Bank personal information leak incident, the security industry said on the 2nd that it had examined attack infrastructure believed to have targeted the bank.
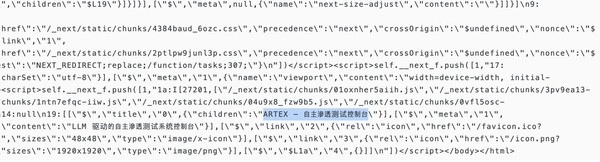
Traces of a Chinese-language AI tool were found in Credential Stuffing infrastructure believed to have targeted Shinhan Bank, and some web server HTML titles were confirmed to contain the string 'ARTEX — Autonomous Penetration Testing Console.'
The Financial Security Institute said it discovered AI agent-based attacks targeting domestic financial companies this year, and that hackers used the DeepSeek AI agent to find Oracle WebLogic and simultaneously put more than 300 domestic and overseas financial companies in the attack scope.
As a personal information leak incident at Shinhan Bank unfolded, the security industry announced on the 2nd that it had examined attack infrastructure believed to have targeted the bank.
During the process, traces of a Chinese-language AI tool were found in infrastructure for a Credential Stuffing attack believed to have targeted Shinhan Bank. Credential Stuffing is a method in which acquired account and password information is tried across multiple services.
The HTML title of some web servers contained the string "ARTEX — Autonomous Penetration Testing Console." The string is interpreted as meaning "AI autonomous penetration testing console."
Moon Jong-hyun, head of Genians Security Center, disclosed the related details on LinkedIn. Moon said he had checked the HTML title of the web server used for the attack access, and that the expression suggested ARTEX AI may have been operating within the infrastructure. He also raised the possibility that an AI tool developed in Chinese was used in the hacking.
ARTEX AI is an autonomous penetration testing system based on a large language model (LLM), and its development was centered in the Chinese-language sphere. The system was released as open source on GitHub in July 2026, and it is structured to be independent of any specific AI model. It is also introduced as having functions that automate attack-target information gathering, vulnerability discovery, and vulnerability verification by connecting LLMs such as OpenAI and Anthropic through APIs.
Moon said the apparent purpose of ARTEX AI is to support security checks and penetration testing. He added that the technology is a double-edged sword. Moon pointed out that while the system can be used as a penetration testing tool in authorized security verification environments, it can become a means of maximizing cyberattack efficiency when used by attackers.
However, whether ARTEX AI was actually used in the Shinhan Bank hacking has not been confirmed through official sources such as the financial authorities or Shinhan Bank.
The Financial Security Institute observed AI-enabled cyberattacks targeting the financial sector in actual financial institutions and said it discovered AI agent-based attacks targeting domestic financial companies this year. Hackers used the DeepSeek AI agent to find Oracle WebLogic, one of the assets scanned by the attack, and put more than 300 domestic and overseas financial companies in the attack scope at once.
The attack proceeded by installing a web shell on vulnerable systems and further probing internal assets, and the Financial Security Institute detected and blocked it at the stage where it attempted to download additional malware for further attacks. According to the institute's analysis, the attack was not fully automated, but it was found to have carried out activity close to a targeted attack against multiple financial firms, and its difference from previous hacking was also summarized as its activity being close to a targeted attack against multiple financial firms.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241984
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.