AIspere Accelerates AI-Driven Security Operations Automation with Microsoft Foundry
IT DAILY ·
✦ AI Summary
AIspere announced on the 18th that it had advanced its AI-based threat exposure management product AITEM with AI agent technology based on Microsoft Foundry.
AITEM is based on CTEM, Continuous Threat Exposure Management, and supports response prioritization by identifying and analyzing externally exposed assets, vulnerabilities, and threat intelligence.
The applied AI agents link and organize information from multiple security tools and databases, and organize review targets and related information when new vulnerabilities or asset changes occur.
AIspere announced on the 18th that it had advanced its AI-based threat exposure management product, “AITEM (AI Threat Exposure Management),” with AI agent technology based on “Microsoft Foundry.” The upgraded capability is AI-based security operations automation.
AITEM is a product developed based on CTEM, Continuous Threat Exposure Management. The product is structured to identify and analyze externally exposed assets, identify and analyze vulnerabilities, and identify and analyze threat intelligence to support response prioritization.
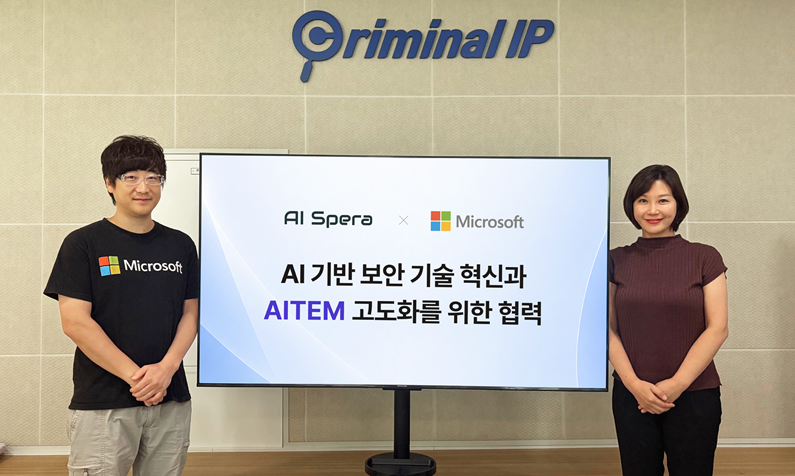
AIspere said it had automated repetitive security operations processes by applying AI agents to CTEM. The photo shows AIspere CEO Kang Byung-tak and MS ASEAN leader Song Joo-hyun.
The factor contributing to operational automation is the AI agent environment in Microsoft Foundry. The Foundry functions based on MS Azure support enterprises in building, deploying, and operating AI applications and agents. In this environment, the AI agents applied to AITEM take on the role of linking and organizing information distributed across multiple security tools and databases.
AITEM uses the results of AIspere’s cyber threat intelligence, “Criminal IP,” from its global internet data collection and analysis, as well as its technology for identifying and analyzing externally exposed assets. Through this, it identifies externally exposed assets, vulnerable services, certificate issues, and security misconfigurations that companies may not be aware of, from an external attacker’s perspective. In addition, AITEM’s AI agents connect asset information with vulnerabilities and threat intelligence.
When a new vulnerability is disclosed or asset information changes, AITEM’s AI agents organize the review targets for security staff, along with related information and the basis for analysis. As a result, security staff’s inquiry and analysis workload decreases. The core of AITEM lies in automating repetitive analysis and response review processes by linking data from multiple security systems.
CEO Kang Byung-tak of AIspere said that, as the complexity of corporate digital environments increases, the burden of continuously checking and analyzing externally exposed assets and related security information is also growing. As a way to reduce this burden, he said AIspere will combine Microsoft Foundry-based AI agent technology with AIspere’s global threat intelligence to support automation of security operations tasks and help security staff focus on reviewing actual risks and formulating response strategies.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241725
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.