AutoCrypt Reveals Mediatek Chipset Security Flaw, Registers CVEs
IT DAILY ·
✦ AI Summary
It was disclosed on the 29th that AutoCrypt had discovered security vulnerabilities in MediaTek chipsets and Little Kernel (LK), the open-source embedded kernel, and reported them.
AutoCrypt's red team conducted security research in the first half of this year on MediaTek's SoC and LK, and reported the vulnerabilities to MediaTek and the LK project after discovering them.
The reported vulnerabilities were registered with CVE, and AutoCrypt reported vulnerabilities registered as CVE-2026-20466 and CVE-2026-50971 through MediaTek's bug bounty program and received rewards.
It was disclosed on the 29th that AutoCrypt had discovered security vulnerabilities in Mediatek chipsets and an open-source embedded kernel and reported them. AutoCrypt's red team conducted security research in the first half of this year on semiconductor company MediaTek's SoC, and also on Little Kernel (LK), the open-source embedded kernel used in that boot environment. After identifying vulnerabilities during the research, the team reported them to MediaTek and the LK project.
The reported vulnerabilities were later registered with CVE (Common Vulnerabilities and Exposures).
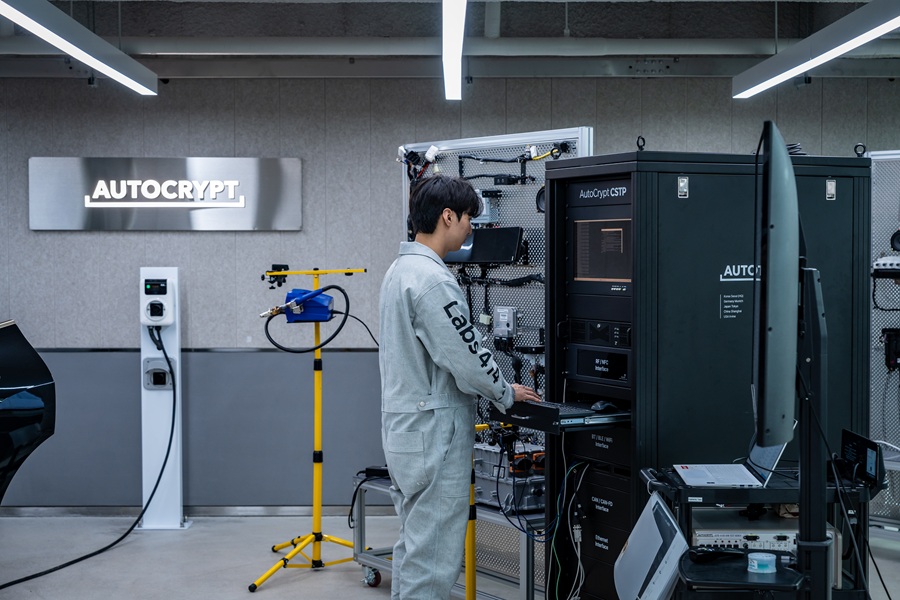
The person in the photo is an AutoCrypt red team employee. The photo was taken at AutoCrypt's Physical AI Security Research Center in Samseong-dong, Gangnam District, Seoul.
AutoCrypt found vulnerabilities in MediaTek and the LK project and reported them separately. AutoCrypt participated in MediaTek's bug bounty program and reported vulnerabilities that were registered as CVE-2026-20466, and it also discovered an additional vulnerability that was registered as CVE-2026-50971. In the process, AutoCrypt received bug bounty rewards.
AutoCrypt said it reported the vulnerabilities it found to the manufacturer and the open-source community, resulting in security updates. It also said that the details it reported to the LK project were reflected in the open-source project's official patch. AutoCrypt said it carried out the Responsible Disclosure process throughout the entire sequence.
Kim Deok-soo, CEO of AutoCrypt, said the significance of this research lies in expanding the scope of security research beyond automobiles to software and hardware in embedded environments. He added that the company will continue working with manufacturers and the open-source community to help ensure the swift remediation of vulnerabilities it discovers.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241888
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.