Autocrypt Finds Security Vulnerabilities in MediaTek Chipset During Research
TECHWORLD ·
✦ AI Summary
Autocrypt's red team said it discovered security vulnerabilities while researching MediaTek's SoC and the open-source embedded kernel LK used in the boot environment.
The identified vulnerabilities were reported to MediaTek and the LK project. MediaTek assigned the issue CVE-2026-20466, and an additional vulnerability was given CVE-2026-50971.
Autocrypt participated in MediaTek's bug bounty program and received a reward, and the LK project-related reports led to upstream patches and security updates.
BizCrushWant to follow Korean talks and live streams in real time?Try CapCrush on the web
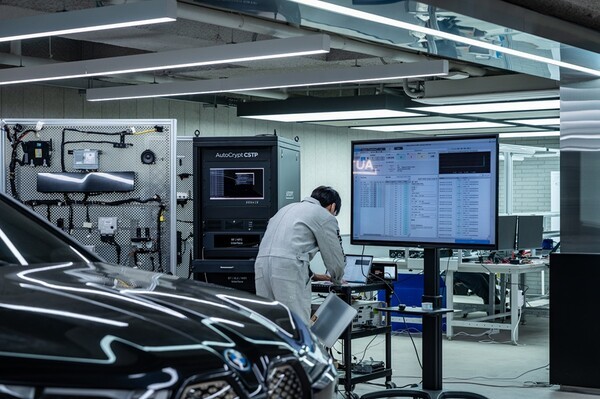
Autocrypt said on the 29th that its red team discovered security vulnerabilities in MediaTek chipsets and Little Kernel (LK), the open-source embedded kernel used in the boot environment of MediaTek's SoCs, while researching them in the first half of this year. The discoveries were made during a security research effort by Autocrypt's red team.
Autocrypt's red team reported the identified vulnerabilities to MediaTek and the LK project. MediaTek later assigned the issue CVE-2026-20466, and the vulnerability was registered as a CVE. An additional vulnerability was assigned CVE-2026-50971.
Autocrypt participated in MediaTek's bug bounty program and received a bounty reward. The company said the CVE assignment and the bug bounty reward recognized the results of its research and demonstrated its security research capabilities.
Reports related to the LK project led to official upstream patches in the open-source project, and the discovered vulnerabilities were reported to the manufacturer and the open-source community. The reports resulted in actual security updates, and the process was carried out under a Responsible Disclosure procedure.
Autocrypt is a physical AI security company that grew out of automotive cybersecurity. The company has continuously strengthened its adversary-focused system analysis capabilities and is recently expanding its research into a variety of embedded environments.
Kim Deok-soo, CEO of Autocrypt, said the significance of the research lies in the expansion of its scope beyond automobiles to the low-level software and hardware security areas of diverse embedded environments. He also said the company plans to continue working with manufacturers and open-source communities and to pursue responsible security research that encourages the rapid remediation of discovered vulnerabilities.
Source: TECHWORLD · Kim Hye-jin
Original: https://www.epnc.co.kr/news/articleView.html?idxno=407454
References
This article was produced with the help of an automated content generation algorithm.
Source: TECHWORLD
View originalThis article was summarized and organized by BizCrush based on the original article from TECHWORLD. For exact quotations and full details, please refer to the original article.
Keep reading
BizCrush