8 More Companies File Breach Reports After Musinsa as Government Probe Continues
IT DAILY ·
✦ AI Summary
At around 9 p.m. on the 1st, the Ministry of Science and ICT and KISA received an email from a person believed to be a hacker. The ministry shared the tip with relevant agencies the next day and identified private companies through report analysis, notifying them of vulnerabilities and signs of intrusion. As a result, 8 additional companies were found to have filed reports after Musinsa, bringing the total to 9.
After a tip alleging a hack of the online fashion platform Musinsa was received, the government shared the information with relevant agencies and analyzed reports to identify related private companies, according to documents submitted to Rep. Lee Joo-hee of the Democratic Party of Korea by the Ministry of Science and ICT and the Korea Internet & Security Agency (KISA), which were made public on the 23rd.
At around 9 p.m. on the 1st, the Ministry of Science and ICT and KISA received an email from a person believed to be a hacker. The email included information on security vulnerabilities in the private, financial, public and defense sectors, and the informant claimed that Musinsa had been hacked.
The ministry shared the tip with relevant agencies, including the Ministry of National Defense, the National Intelligence Service and the Financial Supervisory Service, the next day. It then identified private companies through an analysis of the report and notified the companies of vulnerabilities and signs of intrusion. The ministry and KISA also guided the companies on how to file reports.
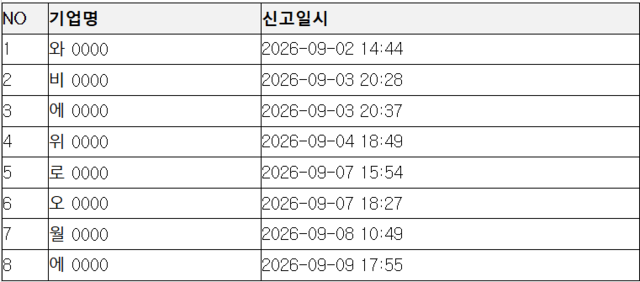
As a result, 8 additional companies were found to have filed reports after Musinsa, and the government launched an investigation following their breach reports. The specific cause of the incident and the scale of damage were not disclosed.
After Musinsa reported a breach on the 28th, before the tip was received, 8 companies filed breach reports from the 2nd to the 9th. That brought the total number of reporting companies, including Musinsa, to 9. Rep. Lee said public anxiety has deepened as 8 companies filed additional reports after Musinsa.
Separately, Musinsa, the operator of 29CM, said 29CM discovered unusual external access targeting an order information inquiry linkage function (API) on Aug. 27. It then confirmed that some customer information from 29CM had been leaked, and said the leaked personal information amounted to about 159,000 cases. By category, customer names accounted for 138,841 cases, while names plus email addresses, mobile phone numbers and delivery information were leaked in 21,011 cases.
KISA is providing technical support to the companies that filed reports and is also analyzing the cause of the incidents. However, the other reported cases are still under investigation, so the scale of damage remains undisclosed and whether personal information was leaked has also not been disclosed.
Rep. Lee said the government plans to support efforts to determine the scale and cause of the damage through its investigation. He added that it also plans to verify the implementation of checks across the financial, public and defense sectors.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241832
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.