[Information Security Solutions Conference] “The Core of Microsegmentation Is Trust and Access Control”
IT DAILY ·
✦ AI Summary
At the 2026 Information Security Solutions Conference, Choi Young-cheol, CEO of SGA Solutions, presented strategies for redesigning cybersecurity frameworks in the AI era, along with server security and microsegmentation-based security architecture.
He explained that microsegmentation is a technology for strengthening internal controls against AI security threats, and that it controls the entire internal environment, including servers, VMs and containers, down to the levels of trust, privileges and behavior.
He also said microsegmentation is a core element of a zero-trust architecture and a damage-minimization strategy designed to block the internal spread of damage after a breach.
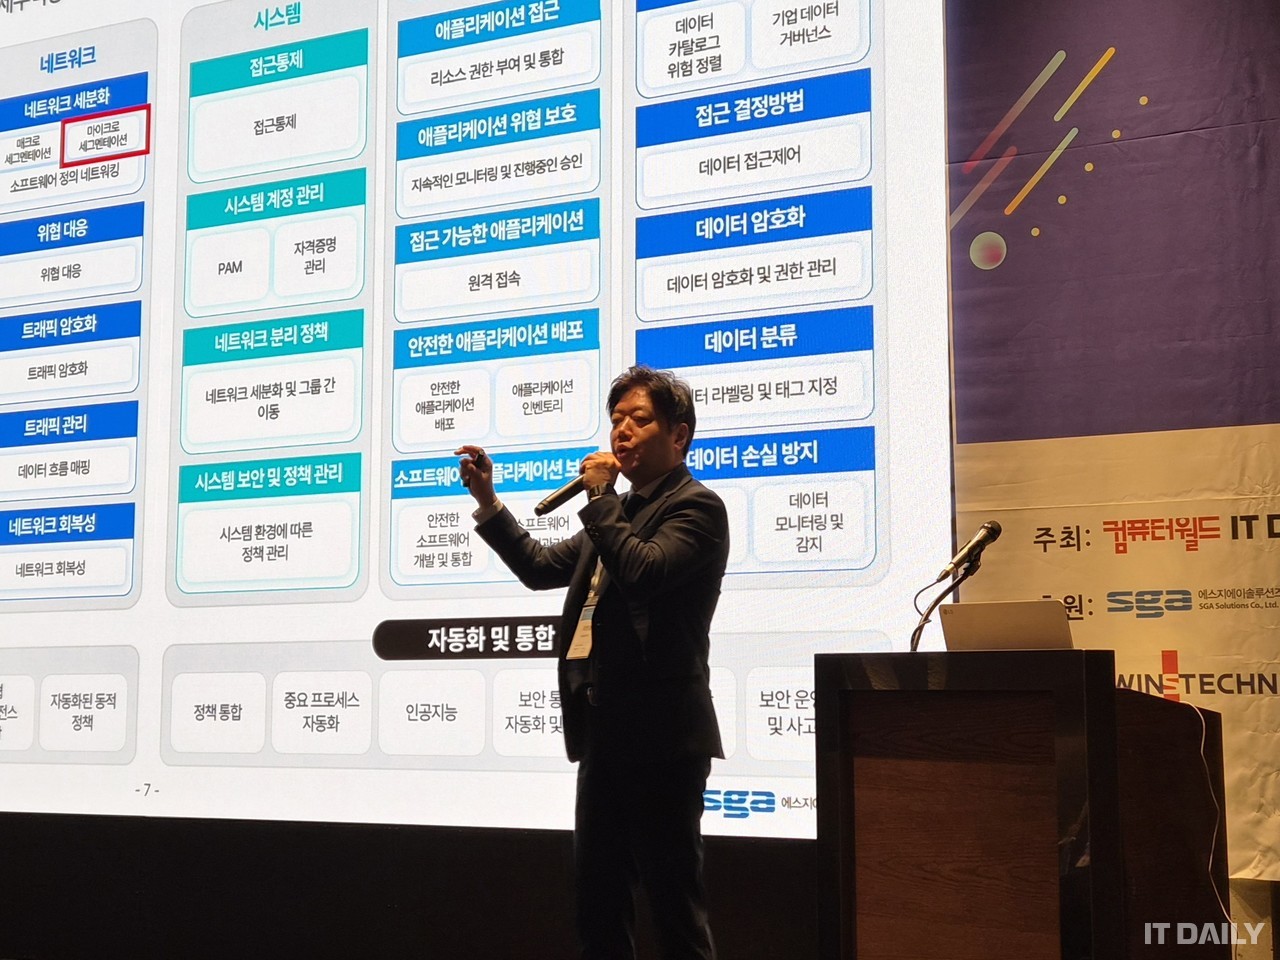
Choi Young-cheol, CEO of SGA Solutions, gave a presentation at the 2026 Information Security Solutions Conference, held on the 9th at L Tower in Yangjae-dong, Seoul, on redesigning cybersecurity frameworks in the AI era and on security deployment strategies based on server security and microsegmentation. The photo shows Choi Young-cheol speaking, and was taken by reporter Kim Ho-jun.
Choi said microsegmentation is drawing attention as a technology for strengthening internal controls to respond to AI security threats. He explained that microsegmentation does not simply mean a technology that divides network and system domains and prevents attack spread.
He added that the scope of microsegmentation covers the entire internal environment, including servers, VMs and containers. He also said it is a method of finely dividing and controlling trust, privileges and behavior levels.
Microsegmentation is one of the three core elements of a zero-trust architecture. In the past, security was centered on internal and external boundaries, which made it strong at defense before infiltration but limited in responding after infiltration. Accordingly, as security incidents occur frequently, microsegmentation has emerged as a damage-minimization strategy to block the internal spread of damage after a breach by separating communications by unit, such as business, system and workload, instead of relying on physical internal-external boundaries.
Choi said it is difficult to determine the measures needed to implement microsegmentation. He also noted that even when solutions are presented as microsegmentation, the functions they provide are often different. Choi explained this based on the 'Zero Trust Reference Architecture (ZTRA)' announced by the U.S. Department of Defense (DoD) in 2022.
Under the ZTRA framework, the basic principle of microsegmentation is to first block and control all traffic between servers and services, Choi explained. He added that if internal movement is necessary, strict authentication procedures are required.
The first separation criterion in ZTRA is network-centric macrosegmentation. ZTRA is structured to additionally apply microsegmentation to areas that cannot be protected by macrosegmentation alone. A representative use case is VMs. Unlike physical servers, VMs are difficult to protect with firewalls, each VM runs on the same infrastructure, and the boundaries between VMs are also characterized by logical separation. For this reason, it is necessary to analyze and distinguish points where boundaries are unclear, and microsegmentation is the means to do so.
Choi explained that many solutions focus on applications and APIs. He added that the scope of microsegmentation goes beyond those two areas and spans the entire system, and that communications, as well as trust, privileges and behavior, need to be granularly controlled. Microsegmentation is closely linked to zero trust.
SGA Solutions' 'SGA ZTA Platform' applies microsegmentation across three layers — servers, VMs and containers — and uses different control methods for each layer. The platform is characterized by extending communications within the microsegmentation scope to trust and privileges. On the server side, it applies a host firewall to protect internal system communications, blocks threats first, allows access only to authenticated users, and limits the number of concurrent session connections to a certain level.
In the VM workload area, granularity is applied on the premise that even VMs within the same infrastructure do not share the same level of trust. To do this, a policy enforcement point (PEP) is deployed for each workload, and application execution and user access are controlled individually. In addition, unauthorized movement between workloads is restricted.
In the container area, the approach is linked to the development lifecycle and applied across the entire process of development, deployment, execution and operations. In this process, verification and control are performed at each stage of resources, as well as at each stage of Runtime behavior. It is also being offered in the form of a cloud-native application protection platform (CNAPP), alongside the trend toward integration of workloads and containers.
Choi said AI has increased attack speed and expanded attack scale, and he outlined a response direction based on the reality that it is impossible to avoid hacking. Accordingly, he said the defense objective should be to minimize damage rather than avoid breaches, and that the strategy should focus on microsegmentation.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241493
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.