Sparrow Holds Application Security Summit 2026
IT DAILY ·
✦ AI Summary
Sparrow held the "Application Security Summit 2026" at the Fairmont Ambassador Seoul in Yeouido on the 27th.
The event was attended by chief information officers (CIOs), chief information security officers (CISOs), and more than 30 leaders from the industrial sector.
The event highlighted measures to strengthen SW supply chain security, the importance of SBOM, and open-source component management and vulnerability response systems.
Sparrow held the "Application Security Summit 2026" at the Fairmont Ambassador Seoul in Yeouido on the 27th. The event is Sparrow's annual breakfast seminar.
The event was aimed at chief information officers (CIOs) and chief information security officers (CISOs), and this year's event drew more than 30 leaders from the industrial sector.
This year's theme was "A Roadmap for Strengthening SW Supply Chain Security: From Response to Strategy." The event focused on measures to strengthen SW supply chain security.
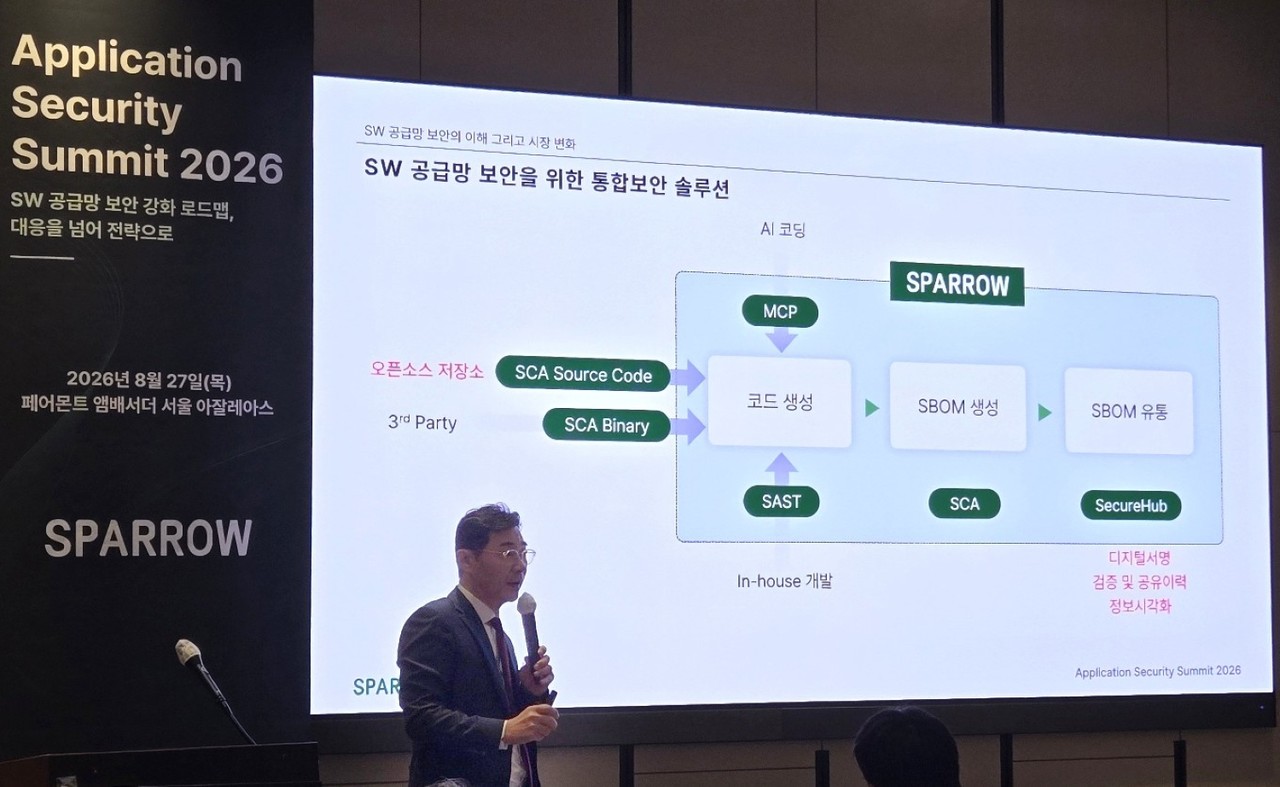
On the day, Jang Il-soo, CEO of Sparrow, took part as the keynote speaker and explained trends in SW supply chain security regulations while emphasizing the importance of the software bill of materials (SBOM). A photo from the event, taken on the 27th at the "Application Security Summit 2026," shows Jang Il-soo, CEO of Sparrow, delivering his presentation, and the photo was provided by Sparrow.
Jang said that SBOM requirements are rising in major countries such as the U.S., the EU, and Japan, and explained that securing SBOM accuracy and reliability is becoming increasingly important. He also said there is a need for a management framework covering the entire process from generation to verification and distribution, and outlined practical strategies including SBOM lifecycle management, establishing a vulnerability response system based on SBOM, and secure distribution based on digital signatures and verification.
Yeo Goo-yong, head of business at Sparrow, introduced ways to respond to the government's roadmap for strengthening SW supply chain security. Yeo emphasized security by design across the entire SW development lifecycle and shared use cases for "Sparrow Enterprise." These included establishing a system for managing the use of open-source components and a system for managing vulnerabilities in open-source components.
Yun Jong-won, CTO of Sparrow, emphasized the importance of proactively blocking the introduction of vulnerable components in such a system. He also stressed the importance of setting mitigation priorities for discovered vulnerabilities based on risk and impact.
The CTO explained that Sparrow applies component introduction control policies starting at the open-source intake stage and provides a function to prevent the use of vulnerable components. He added that Sparrow uses AI to provide a function that suggests mitigation priorities by considering asset criticality and vulnerability risk.
The CTO said Sparrow recently added VEX and Vulnerability Exploitability eXchange capabilities, which help determine whether vulnerabilities actually have an impact. He also said the company plans to further enhance its products by offering EPSS and Exploit Prediction Scoring System in the future.
Source: IT DAILY · Kim Ho-jun
Original: https://www.itdaily.kr/news/articleView.html?idxno=241236
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
View originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.