[Audit] LGU+ Under Scrutiny Over Disposal of Intrusion-Affected Servers and OS Reinstallation
IT DAILY ·
✦ Resumen de IA
During the National Assembly’s Science, ICT, Broadcasting and Communications Committee audit, the circumstances surrounding LGU+’s disposal of suspected hacked servers and OS reinstallation last year were discussed.
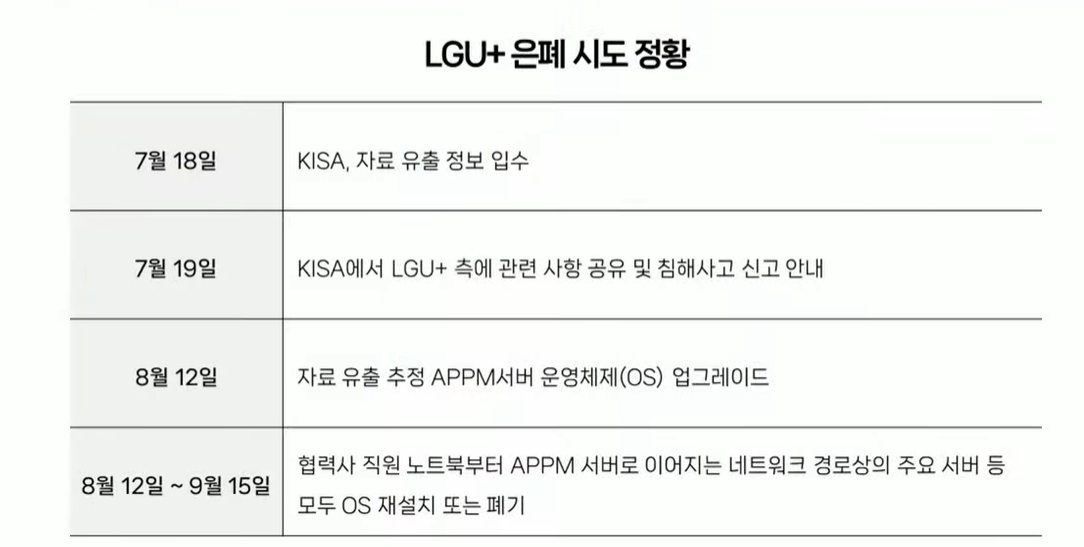
LGU+ disposed of the suspected intruded server on July 31 after receiving KISA’s notice on July 19, and reinstalled the OS on August 12.
CISO Hong Gwan-hui said the server image was created after KISA’s notification, while the government-private joint investigation team officially announced that the OS had been reinstalled and that no traces of intrusion or attack path could be confirmed.
The National Assembly’s Science, ICT, Broadcasting and Communications Committee held an audit on the 6th, where the disposal of suspected hacked servers and OS reinstallation at LGU+ last year was raised. Lawmakers summoned LGU+ Chief Information Security Officer (CISO) Hong Gwan-hui as a witness to question him about the company’s response to the intrusion incident.
Lawmakers Lee Hoon-gi and Han Jun-ho questioned CISO Hong Gwan-hui about the circumstances surrounding the disposal of the servers and the OS reinstallation at the time of the intrusion incident. The focus of the questioning was the process behind the server disposal and OS reinstallation during the incident.
On July 19 last year, LGU+ was notified by the Korea Internet & Security Agency (KISA) of suspected hacking signs on an account management (APPM) server. This was cited at the audit as the starting point of the intrusion-response process.
LGU+ then physically disposed of the suspected intruded server on July 31. It was noted that 12 days had elapsed between the notification and the server disposal.
LGU+ was also found to have reinstalled the OS on the suspected intruded server on August 12. This was presented during the audit in the course of questions from lawmakers Lee Hoon-gi and Han Jun-ho (source: Han Jun-ho’s office).
In the first row, the CISO of the three major telecom companies are waiting. The photo was taken by reporter Seong Won-young.
The circumstances under which the government and the Personal Information Protection Commission separately requested investigations were also presented in connection with the server disposal and OS work. The Ministry of Science and ICT requested an investigation on December 9, and the request covered LGU+’s server disposal and related issues. The confirmed matters include whether it constituted obstruction of the performance of official duties by abuse of authority.
The Personal Information Protection Commission also requested an investigation from law enforcement on July 29 this year. The reason given was that the server disposal made it difficult to determine how the personal information was leaked.
The National Assembly then focused on whether OS work was carried out before preserving the original state after KISA’s notice of intrusion signs. Lawmaker Han Jun-ho pointed out that OS reinstallation took place after KISA’s notice of intrusion signs. He asked whether KISA’s July 19 notification had been received and also asked whether OS work had been carried out on the APPM-related server on August 12. He also asked, in effect, that when the possibility of intrusion is reported, it is generally standard to preserve the original state before reinstalling the OS.
In response, LGU+ explained the limits of preservation measures and the nature of the materials it submitted. CISO Hong said that materials were preserved where necessary and also explained that there were some shortcomings. He added that the materials submitted to KISA were not simple backup images but server images that could be used for forensics.
The questioning began with a lawmaker asking when the server image was created. In response, Hong said the server image was created after KISA’s notification.
The lawmaker then pointed out that the original was preserved and the image was submitted. This point was raised in relation to the government-private joint investigation team’s official announcement.
In its official announcement, the government-private joint investigation team said that the OS had been reinstalled, that no traces of intrusion could be confirmed, and that the attack path could not be identified. The questioning then continued into whether the timing of the server image creation was consistent with the investigation team’s announcement.
Lawmaker Lee Hoon-gi then asked what measures would be taken if LGU+’s fault were recognized in connection with the server disposal, and whether penalty fees would be waived under the terms and conditions. In response, Executive Vice President Hong Gwan-hui said the company would review all possible measures and proceed after internal discussions.
Source: IT DAILY · Seong Won-young
Original: https://www.itdaily.kr/news/articleView.html?idxno=242033
References
This article was produced with the help of an automated content generation algorithm.
Source: IT DAILY
Ver originalThis article was summarized and organized by BizCrush based on the original article from IT DAILY. For exact quotations and full details, please refer to the original article.